Configure SSO with Azure AD
This article covers configuring SSO with Azure AD as your identity provider.
Before you start
You need the Admin role on the LMS and Azure AD tenant admin rights.
Step 1 — Copy the LMS SP metadata
Open Configuration → Settings → SSO and copy the metadata URL. You paste this into Azure AD's enterprise app configuration.
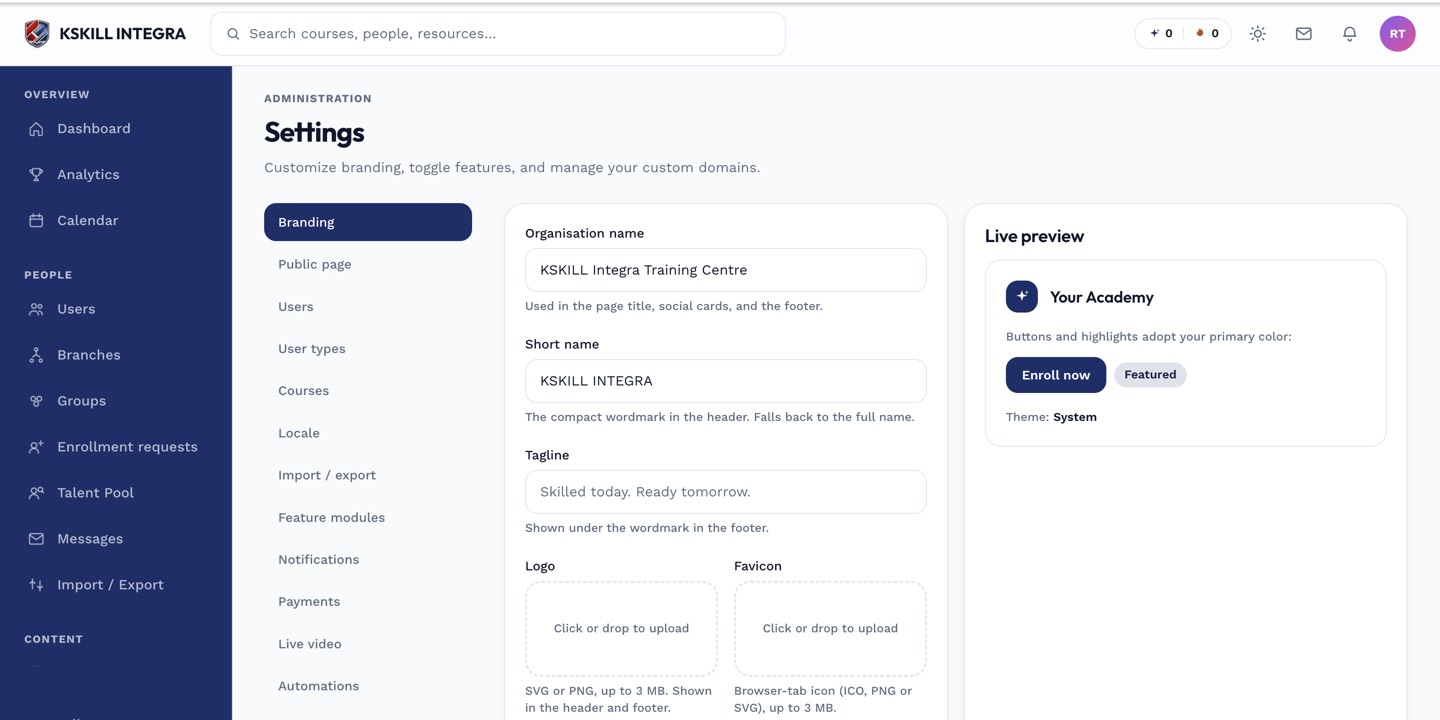
The Settings page is the single home for every tenant-level toggle.
Step 2 — Create the Azure enterprise app
In Azure Portal, create a new enterprise app for SAML SSO. Paste the SP metadata URL. Under attributes, map user.mail to email, user.givenname to firstName, user.surname to lastName. Assign a test group and download the federation metadata XML.
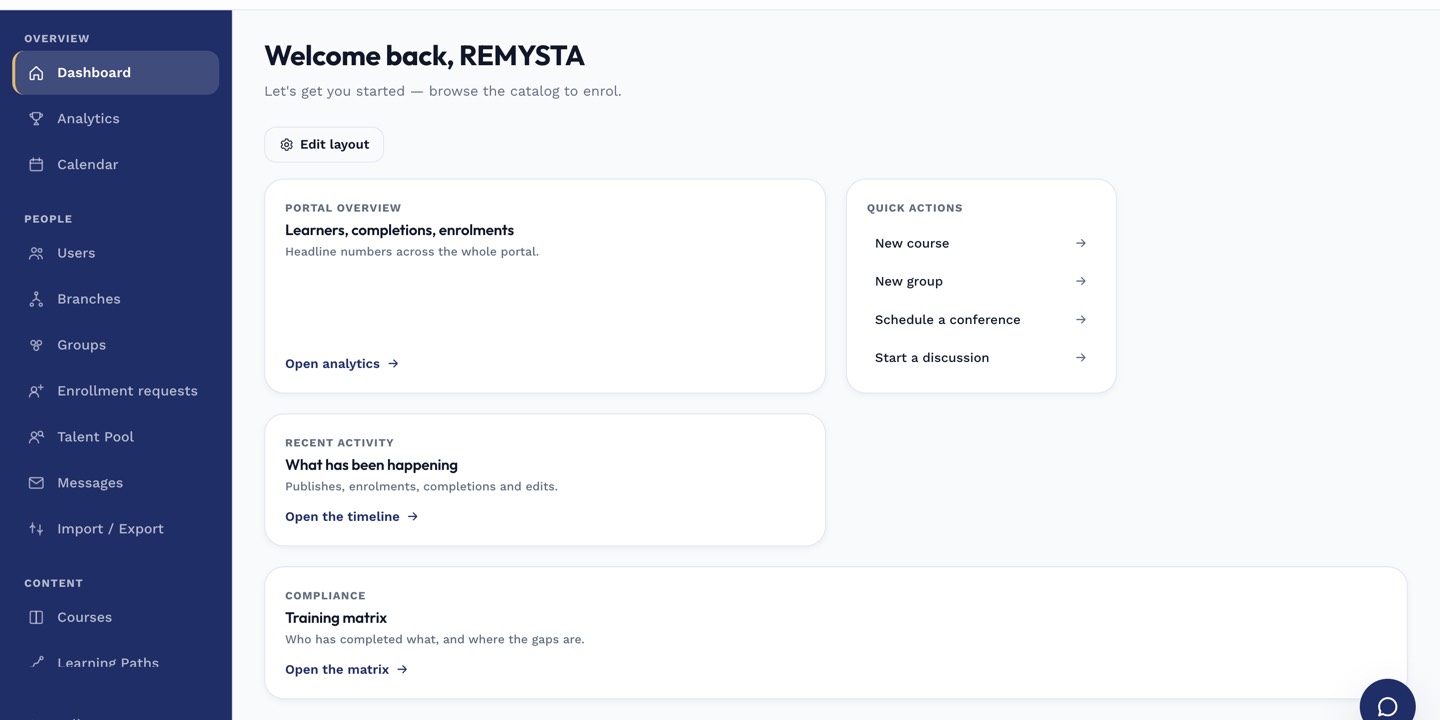
The left rail is the anchor for every admin task; every screen you visit starts with a click here.
Step 3 — Wire the IdP metadata back
Back on the LMS SSO page, upload the Azure metadata XML. Save. Click Test SSO — verify the attributes come through correctly. Flip Require SSO when confident.
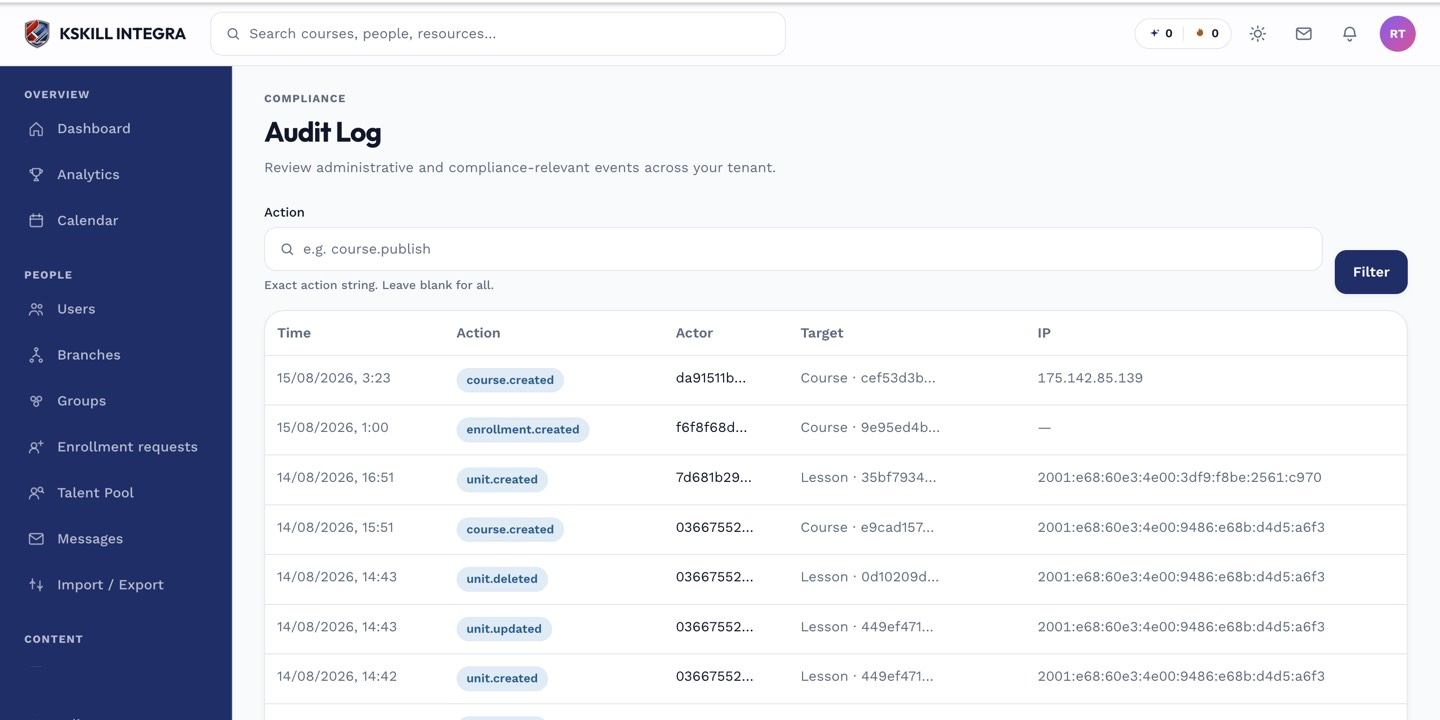
The audit log is your immutable record of who did what.
Notes
- Azure AD supports auto-provisioning via SCIM — see the SCIM article for that separate wiring.
- Conditional Access policies apply to the SAML app; test with your restrictive policies in place.